The attacker must already know a file’s exact name and path and cannot list what the directory holds. Atlassian disclosed the flaw, CVE-2026-21589, on October 5, rated it 9.3 out of 10, and
This post was originally published on The Hacker News.
The attacker must already know a file’s exact name and path and cannot list what the directory holds. Atlassian disclosed the flaw, CVE-2026-21589, on October 5, rated it 9.3 out of 10, and
This post was originally published on The Hacker News.
That’s according to a report from Reuters, citing two sources familiar with the matter.
“To date, our review has determined that the incident occurred as the result of a security failure
This post was originally published on The Hacker News.
They used a private Danish company’s lawful right to look up records in the Central Person Register (CPR). The ministry has told people never to
This post was originally published on The Hacker News.
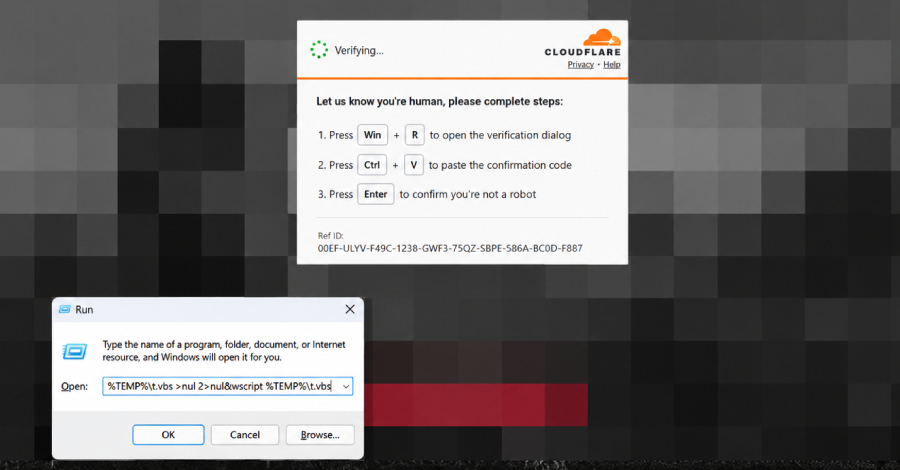
“Instead of downloading and executing remote payloads like the typical attack pattern, in this attack, the websites pre-fetch a script payload into the browser cache disguised as a PNG file,” the Microsoft Threat Intelligence team said in a post on X.
This post was originally published on The Hacker News.
OpenAI is preparing to add invisible watermarks to text generated by ChatGPT and Codex in the European Union. […]
This post was originally published on BleepingComputer.

This post was originally published on Dark Reading.
Hackers are actively scanning for a Rejetto HFS weak signing key vulnerability, tracked as CVE-2026-61500, that allows session forgery, account takeover, and remote code execution (RCE). […]
This post was originally published on BleepingComputer.
Italy’s Data Protection Authority (GPDP) has fined IQVIA €7 million ($7.8M) over poor data-processing practices that the agency says could have put roughly one million patients at risk of data exposure and de-anonymization. […]
This post was originally published on BleepingComputer.

The vulnerability, tracked as CVE-2026-96940, is rated 8.8 on the CVSS scoring system.
“Weak authorization in Microsoft Exchange Server allows an authenticated attacker to elevate privileges over a
This post was originally published on The Hacker News.

This post was originally published on Dark Reading.