Skip to content

proxyblue.yourcyber.news

  • Passing the Baton: Dark Reading Names New Editor-in-Chief

    Passing the Baton: Dark Reading Names New Editor-in-Chief

    Fahmida Y Rashid will keep the momentum going as she leads Dark Reading.

    This post was originally published on Dark Reading.
    October 12, 2026
  • Microsoft: Windows 11 23H2 reaches end of support in 30 days

    Microsoft has reminded customers that systems running Windows 11 23H2 Enterprise, Education, and IoT Enterprise editions will stop receiving security updates next month. […]

    This post was originally published on BleepingComputer.
    October 12, 2026
  • Bring Your Own Agent: Your Employees’ Assistants Are Already Logged In

    Bring Your Own Agent: Your Employees’ Assistants Are Already Logged In

    The personal AI agents rollout is going about as smoothly as expected: Amazon now blocks Meta’s Muse because it doesn’t identify itself as a bot while browsing; Instinct keeps raising privacy concerns; and the horror stories from pretty much every personal AI agent keep piling up.

    Regardless, the tech world is mesmerized by the capabilities and potential of these services. Less than a year

    This post was originally published on The Hacker News.
    October 12, 2026
  • Ledger Finds Unauthorized Hardware Implant in CryptoBilis-Sold Wallet Amid Fund Theft Reports

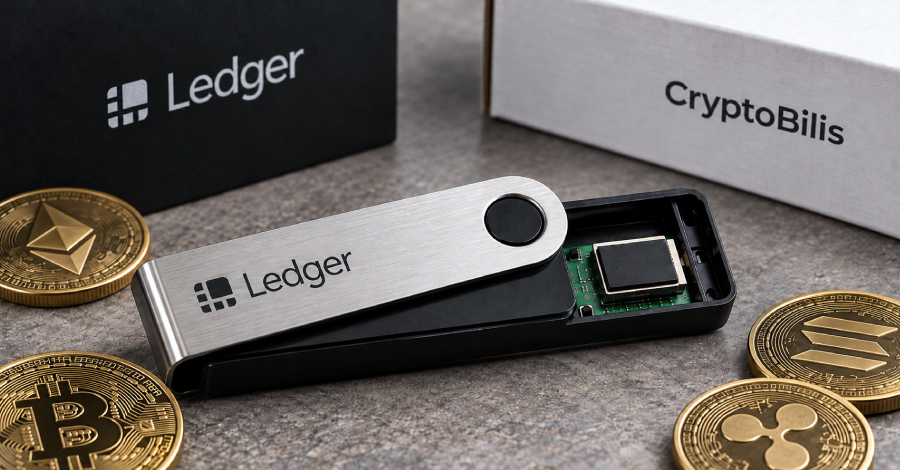
    Ledger Finds Unauthorized Hardware Implant in CryptoBilis-Sold Wallet Amid Fund Theft Reports

    Cryptocurrency hardware maker Ledger has temporarily paused sales of its products via Cryptobilis following reports of stolen funds linked to devices sold by the reseller.

    On Friday, the company said it was investigating reports of loss of funds from users in Southeast Asia who had purchased products from CryptoBilis. The incident is said to have resulted in losses totaling more than $86

    This post was originally published on The Hacker News.
    October 12, 2026
  • Critical SonicWall SMA 1000 Flaw Targeted in 135 Exploitation Attempts After Patch

    Critical SonicWall SMA 1000 Flaw Targeted in 135 Exploitation Attempts After Patch

    Threat actors have been observed exploiting a recently disclosed critical security flaw in SonicWall Secure Mobile Access (SMA) 1000 appliances within days of public disclosure.

    The vulnerability, tracked as CVE-2026-102255 (CVSS score: 10.0), is a case of pre-authenticated server-side request forgery (SSRF) that could allow a remote attacker “to direct the appliance to issue requests on their

    This post was originally published on The Hacker News.
    October 12, 2026
  • Attackers Exploit CVSS 10.0 Bricksforge WordPress Flaw Enabling Unauthenticated RCE

    Attackers Exploit CVSS 10.0 Bricksforge WordPress Flaw Enabling Unauthenticated RCE

    A maximum-severity security flaw impacting the Bricksforge plugin for WordPress has come under active exploitation in the wild, according to Patchstack.

    The critical vulnerability in question is CVE-2026-85097 (CVSS score: 10.0), which allows unauthenticated attackers to upload and execute arbitrary PHP code on vulnerable WordPress websites, resulting in remote code execution (RCE). The

    This post was originally published on The Hacker News.

    October 12, 2026
  • AI-driven security: Why agentic AI is changing cybersecurity

    Agentic AI is transforming cybersecurity — but rogue agents, shadow AI, and third-party risks demand stronger guardrails.

    This post was originally published on Cybersecurity Dive.
    October 12, 2026
  • CyberXero Uses Claude Code in Campaign That Stole Over 628,000 Ukrainian Records

    CyberXero Uses Claude Code in Campaign That Stole Over 628,000 Ukrainian Records

    Cybersecurity researchers have disclosed details of a two-pronged artificial intelligence (AI)-augmented initial access campaign targeting WordPress sites, e-commerce platforms, and critical infrastructure entities in Ukraine.

    The activity, which brings together commodity offensive tools like Cobalt Strike with an AI orchestration layer powered by Anthropic’s Claude Code, has been attributed

    This post was originally published on The Hacker News.

    October 12, 2026
  • Nippon Columbia malware incident exposes 8.6 million karaoke fan records

    Daiichi Kosho, a major Japanese entertainment system maker, disclosed that a malware infection at its contractor, Nippon Columbia, exposed more than 8.7 million customer and employee records. […]

    This post was originally published on BleepingComputer.

    October 11, 2026
  • Cyber exec arrested in case allegedly tied to ShinyHunters hackers

    Canadian cybersecurity executive Edward Dubrovsky has been arrested in Pennsylvania in connection with alleged extortion activity that multiple reports have linked to the FBI’s ongoing crackdown on the ShinyHunters hacking group. […]

    This post was originally published on BleepingComputer.

    October 10, 2026
←Previous Page
1 … 4 5 6 7 8 … 33
Next Page→

proxyblue.yourcyber.news

  • Blog
  • About
  • FAQs
  • Authors
  • Events
  • Shop
  • Patterns
  • Themes

Twenty Twenty-Five

Designed with WordPress