Microsoft says devices running unsupported versions of Windows will stop receiving security updates after next year’s Windows Update certificate rotation. […]
This post was originally published on BleepingComputer.
Microsoft says devices running unsupported versions of Windows will stop receiving security updates after next year’s Windows Update certificate rotation. […]
This post was originally published on BleepingComputer.
Searchlight Cyber, which disclosed the flaw on October 8, says an attacker who recovers the key can redirect the site’s visitors to a copy of the site they control.
This post was originally published on The Hacker News.
Citrix has warned IT administrators to patch systems immediately against a new critical vulnerability affecting NetScaler ADC networking appliances and NetScaler Gateway secure remote access solutions. […]
This post was originally published on BleepingComputer.
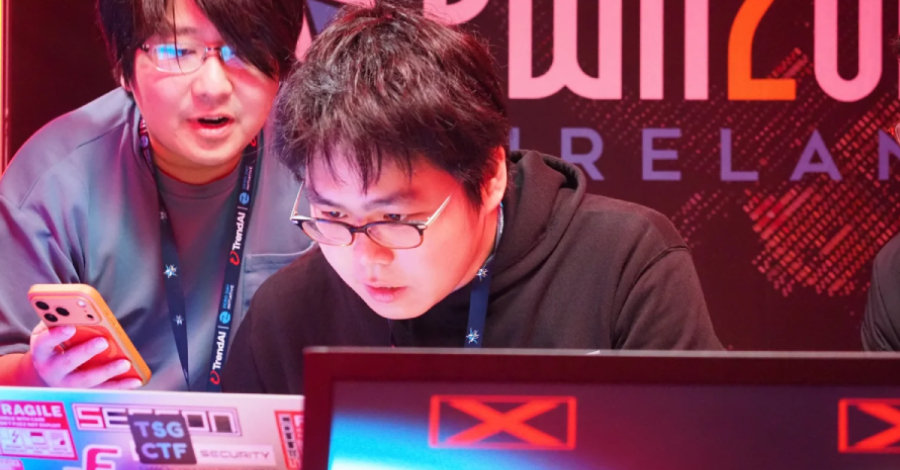
Trend Micro’s Zero
This post was originally published on The Hacker News.
“CVE-2026-107406 is a memory overflow vulnerability that may lead to remote code execution or denial-of-service under specific configuration conditions,” Citrix said.
The vulnerability
This post was originally published on The Hacker News.
To that end, the agencies seized several domains and blocked access to platforms that were used to scan, and in some cases infiltrate, U.S. critical infrastructure. The list of seized
This post was originally published on The Hacker News.
The Pwn2Own Ireland 2026 hacking contest has concluded, with hackers collecting $1,262,000 in rewards after exploiting 98 zero-day flaws. […]
This post was originally published on BleepingComputer.
The FBI has seized seven domains used by Chinese state-sponsored hackers known as Flax Typhoon to operate two hacking tools, MicroScan and FishHub, used in attacks that breached critical infrastructure and other organizations worldwide. […]
This post was originally published on BleepingComputer.
This post was originally published on Dark Reading.
IDC Frontier, a major Japanese cloud and digital infrastructure company, disclosed that its IDCF Cloud service was targeted in a ransomware attack that caused an outage at a data center cluster serving the eastern part of the country. […]
This post was originally published on BleepingComputer.