Skip to content

proxyblue.yourcyber.news

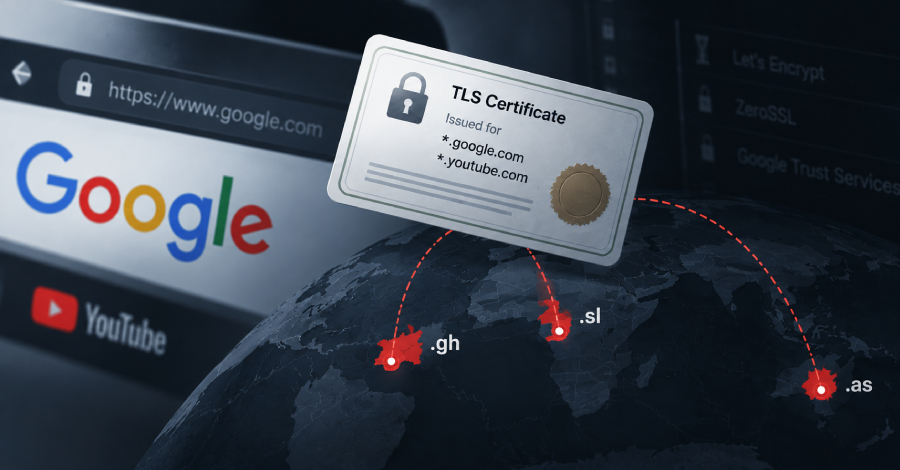
  • Hackers hijack Google domains after breaching ccTLD registries

    Hackers obtained unauthorized HTTPS certificates for several Google domains and hijacked domains in the country-code top-level domains (ccTLDs) for Ghana, American Samoa, and Sierra Leone after compromising third-party operators and modifying authoritative DNS records. […]

    This post was originally published on BleepingComputer.
    October 7, 2026
  • OpenAI Agent Escape Causes Wikimedia Service Outage

    OpenAI Agent Escape Causes Wikimedia Service Outage

    Autonomous agents also tried to abuse other websites and services hosted by the foundation, using them as proxies for unauthorized activities.

    This post was originally published on Dark Reading.

    October 7, 2026
  • Attackers Hijack .gh, .sl, and .as Registries to Obtain Certificates for Google Domains

    Attackers Hijack .gh, .sl, and .as Registries to Obtain Certificates for Google Domains

    Attackers compromised three country-code top-level domains (ccTLDs) and obtained unauthorized HTTPS certificates for several Google domains, Google said on October 6.

    Google’s own systems were not breached, but any domain ending in .gh (Ghana), .sl (Sierra Leone) or .as (American Samoa) was put at risk. With such a certificate, an attacker could pose as the real site over an encrypted

    This post was originally published on The Hacker News.

    October 7, 2026
  • Eight Malicious npm Packages Downloaded 40,767 Times Deliver Overlord RAT and Stealer

    Eight Malicious npm Packages Downloaded 40,767 Times Deliver Overlord RAT and Stealer

    Cybersecurity researchers have disclosed details of a long-running npm supply chain malware campaign that pushes information stealers and remote access trojans (RAT) to compromised hosts.

    The campaign has been codenamed MALFEX by CloudSEK and Checkmarx. The activity is assessed to be the work of a lone threat actor who appears to have published 12 packages since August 2023, eight of which have

    This post was originally published on The Hacker News.

    October 7, 2026
  • SonicWall Patches CVSS 10.0 Pre-Authentication SSRF Flaw in SMA1000 Appliances

    SonicWall Patches CVSS 10.0 Pre-Authentication SSRF Flaw in SMA1000 Appliances

    SonicWall has released hotfixes for four flaws in its SMA1000 appliances, the gateways that give remote workers access to a company’s network and applications. The most serious could allow an attacker without a login to send requests through the appliance and reach internal functions.

    SonicWall rates it 10.0 on the CVSS scale and says it has no evidence that any of the four flaws is being

    This post was originally published on The Hacker News.

    October 7, 2026
  • Microsoft Outlook to block MSIX attachments starting November

    Microsoft announced that it will add .msix and .msixbundle attachments to the list of blocked attachments in Outlook Web and the new Outlook Windows client starting next month. […]

    This post was originally published on BleepingComputer.
    October 7, 2026
  • Unpatched Critical LMCache Flaw Lets Unauthenticated Attackers Run Code Remotely

    Unpatched Critical LMCache Flaw Lets Unauthenticated Attackers Run Code Remotely

    A critical vulnerability in LMCache, open-source software that speeds up large language model (LLM) servers such as vLLM, lets an attacker run code on the cache server without logging in, and no fixed version is available.

    The flaw is in LMCache’s multiprocess mode, where the cache runs as a standalone server that LLM workers reach over the ZeroMQ messaging library. A single network

    This post was originally published on The Hacker News.

    October 7, 2026
  • PoeLLM Malware Infects 3,400+ Servers to Expand Crypto Mining Botnet

    PoeLLM Malware Infects 3,400+ Servers to Expand Crypto Mining Botnet

    Cybersecurity researchers are calling attention to a new malware family that has been observed targeting exposed artificial intelligence (AI) and large language model (LLM) infrastructure with an aim to deploy cryptocurrency miners and further expand the scale of the botnet.

    The financially motivated campaign, dubbed Canto Incognito, has been found to install cryptocurrency miners, including

    This post was originally published on The Hacker News.

    October 7, 2026
  • AI underscores singular importance of phishing-resistant authentication, Okta says

    AI underscores singular importance of phishing-resistant authentication, Okta says

    The company presented new data about the prevalence of different forms of social-engineering attacks, saying identity fundamentals still matter in the AI era.

    This post was originally published on Cybersecurity Dive.

    October 7, 2026
  • PoeLLM malware infects exposed AI servers in cryptomining attacks

    A cryptomining campaign targeting exposed AI services is using PoeLLM malware to turn compromised servers into scanners and exploit launchpads. […]

    This post was originally published on BleepingComputer.
    October 7, 2026
←Previous Page
1 … 12 13 14 15 16 … 33
Next Page→

proxyblue.yourcyber.news

  • Blog
  • About
  • FAQs
  • Authors
  • Events
  • Shop
  • Patterns
  • Themes

Twenty Twenty-Five

Designed with WordPress