Skip to content

proxyblue.yourcyber.news

  • Wikimedia Says OpenAI Agents Tried to Compromise Etherpad and Use Wiki Tools as Proxies

    Wikimedia Says OpenAI Agents Tried to Compromise Etherpad and Use Wiki Tools as Proxies

    The Wikimedia Foundation, which hosts Wikipedia, has confirmed that it has discovered activity by rogue OpenAI agents on its platforms, including unsuccessful efforts to compromise Etherpad, a public note-taking tool, and edit Wikipedia pages.

    “The unauthorized bot activities included edits to our wikis, some unsuccessful attempts to exploit a public note-taking tool we host, and heavy traffic,

    This post was originally published on The Hacker News.
    October 6, 2026
  • Welcome to the Jungle: What We Found Inside 15,465 Public MCP Servers

    Welcome to the Jungle: What We Found Inside 15,465 Public MCP Servers

    In 2024, MCP (Model Context Protocol) set out to become the USB-C of AI: one standard for connecting models, agents, and IDEs to tools and data. The protocol delivered. Thousands of developers built servers, and enterprises plugged them into agent workflows.

    The ecosystem around it fell short. Earlier this year, our team at OX Security,  traced critical vulnerabilities in Anthropic’s MCP

    This post was originally published on The Hacker News.
    October 6, 2026
  • Nikkei discloses breaches of employees’ Microsoft, Google email accounts

    Over the weekend, Japanese publishing giant Nikkei disclosed that unknown attackers recently breached two employee email accounts and used one to send thousands of phishing emails. […]

    This post was originally published on BleepingComputer.

    October 6, 2026
  • Google Pauses OSS Product Bug Bounty Rewards After Surge in Invalid Automated Reports

    Google Pauses OSS Product Bug Bounty Rewards After Surge in Invalid Automated Reports

    Google has stopped accepting product vulnerability reports through its bug bounty program for its open-source software.

    The change, in effect since October 1, means researchers can no longer submit security flaws in the code of projects such as Go, Angular, and Protocol Buffers there for a reward. Reports about supply chain compromises are still accepted, and reports filed before October 1 are

    This post was originally published on The Hacker News.
    October 6, 2026
  • Engineer sentenced for locking over 3,000 devices on employer network

    A former core infrastructure engineer at an industrial company headquartered in New Jersey was sentenced to 32 months in prison for locking thousands of devices on his employer’s network in a ransomware-style attack. […]

    This post was originally published on BleepingComputer.

    October 6, 2026
  • Critical Atlassian Flaw Lets Unauthenticated Attackers Read Known Files Across 8 Products

    Critical Atlassian Flaw Lets Unauthenticated Attackers Read Known Files Across 8 Products

    A critical flaw in 8 Atlassian Data Center products, which customers host themselves, allows an attacker with no login access to read specific files in each product’s web application root directory.

    The attacker must already know a file’s exact name and path and cannot list what the directory holds. Atlassian disclosed the flaw, CVE-2026-21589, on October 5, rated it 9.3 out of 10, and

    This post was originally published on The Hacker News.
    October 6, 2026
  • FBI Removes Accenture Contractor After Patch Failure Led to ShinyHunters Breach

    FBI Removes Accenture Contractor After Patch Failure Led to ShinyHunters Breach

    The U.S. Federal Bureau of Investigation (FBI) has removed an Accenture contractor for their alleged role in a ShinyHunters-breach that led to the theft of personal details of thousands of bureau employees.

    That’s according to a report from Reuters, citing two sources familiar with the matter.

    “To date, our review has determined that the incident occurred as the result of a security failure ​

    This post was originally published on The Hacker News.
    October 6, 2026
  • Denmark Says Attackers Accessed CPR Data for 8.8 Million People via Company Account

    Denmark Says Attackers Accessed CPR Data for 8.8 Million People via Company Account

    Unauthorized parties have gained access to the names, addresses, and personal identification numbers of about 8.8 million people, living and dead, in Denmark’s national population register, the country’s digitalization ministry said on October 5.

    They used a private Danish company’s lawful right to look up records in the Central Person Register (CPR). The ministry has told people never to

    This post was originally published on The Hacker News.
    October 6, 2026
  • ClickFix Smuggles Payloads Through Browser Cache to Bypass Windows Run Limits

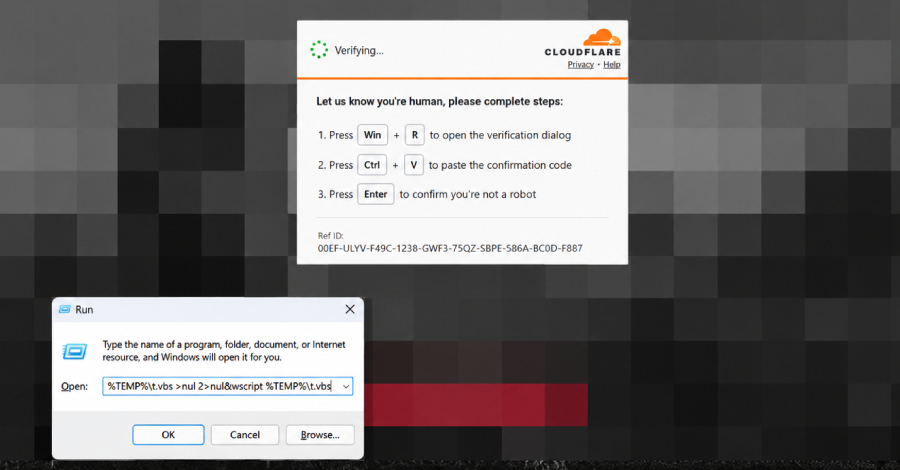
    ClickFix Smuggles Payloads Through Browser Cache to Bypass Windows Run Limits

    A new type of ClickFix attack is using compromised websites to trick users into executing a malicious payload cached in a web browser’s cache.

    “Instead of downloading and executing remote payloads like the typical attack pattern, in this attack, the websites pre-fetch a script payload into the browser cache disguised as a PNG file,” the Microsoft Threat Intelligence team said in a post on X.

    This post was originally published on The Hacker News.

    October 6, 2026
  • OpenAI is adding invisible watermarks to ChatGPT and Codex text in the EU

    OpenAI is preparing to add invisible watermarks to text generated by ChatGPT and Codex in the European Union. […]

    This post was originally published on BleepingComputer.

    October 5, 2026
←Previous Page
1 … 16 17 18 19 20 … 33
Next Page→

proxyblue.yourcyber.news

  • Blog
  • About
  • FAQs
  • Authors
  • Events
  • Shop
  • Patterns
  • Themes

Twenty Twenty-Five

Designed with WordPress