Skip to content

proxyblue.yourcyber.news

  • Microsoft October 2026 Patch Tuesday fixes 1,411 flaws, 3 zero-days

    Today is Microsoft’s October 2026 Patch Tuesday, with security updates addressing a record-breaking 1,411 flaws, including one actively exploited and two publicly disclosed zero-day vulnerabilities. […]

    This post was originally published on BleepingComputer.
    October 13, 2026
  • Microsoft releases Windows 10 KB5126657 extended security update

    Microsoft released the Windows 10 KB5126657 extended security update, which includes this month’s record-breaking October 2026 Patch Tuesday fixes and a few bug fixes and changes. […]

    This post was originally published on BleepingComputer.
    October 13, 2026
  • Microsoft: Windows 11 24H2 Home and Pro reached end of support

    Microsoft announced today that devices running Windows 11 24H2 Home and Pro editions have reached the end of support and will no longer receive monthly security and non-security preview updates. […]

    This post was originally published on BleepingComputer.
    October 13, 2026
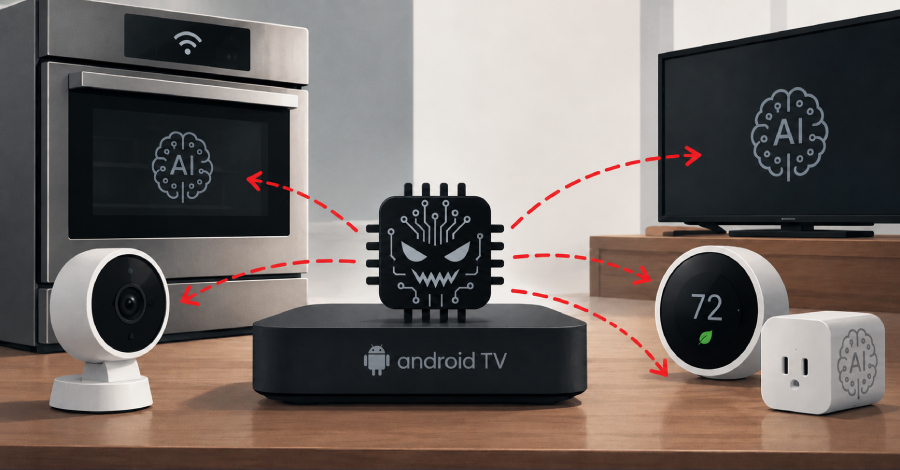
  • Anthropic Warns Small AI Models Could Soon Form Self-Propagating IoT Botnets

    Anthropic Warns Small AI Models Could Soon Form Self-Propagating IoT Botnets

    Small artificial intelligence (AI) models may be months away from developing capabilities to self-replicate on IoT devices like smart ovens and off-brand Android TV boxes, according to a warning from Anthropic.

    The frontier AI lab said small AI models could form autonomous, self-propagating worm botnets that are “challenging to shut down,” since “there’s no centralized point to shut off.”

    This post was originally published on The Hacker News.

    October 13, 2026
  • UK Housing Ombudsman Service investigates ‘security incident’

    The U.K. Housing Ombudsman Service is investigating a third-party IT security incident that impacted its case management system on Tuesday. […]

    This post was originally published on BleepingComputer.
    October 13, 2026
  • Docker Fixes Critical Two-Year-Old Hub Flaw That Let One User Push Images as Another

    Docker Fixes Critical Two-Year-Old Hub Flaw That Let One User Push Images as Another

    A flaw in Docker Hub, the registry where container images are published and downloaded, let one user push, pull, or delete images as another user. Docker fixed the flaw on September 30 and says it found no evidence that anyone exploited it.

    The flaw was in the feature that converts a personal account into an organization, Docker said in a security advisory on October 12.

    This post was originally published on The Hacker News.

    October 13, 2026
  • Windows 11 KB5127648 & KB5126653 cumulative updates released

    Microsoft has released the Patch Tuesday Windows 11 KB5127648 and KB5126653 cumulative updates for versions 26H2/25H2/24H2 and 23H2 to fix security vulnerabilities and bugs, and add new features. […]

    This post was originally published on BleepingComputer.

    October 13, 2026
  • Attacker Chains Three Ivanti Connect Secure Zero-Days for Root Access, Only Two Patched So Far

    Attacker Chains Three Ivanti Connect Secure Zero-Days for Root Access, Only Two Patched So Far

    An attacker chained three zero-day flaws in Ivanti Connect Secure, a VPN appliance, to run commands as root without logging in, security firm Volexity said on October 13. Ivanti has released fixes for two of the flaws and told customers on affected versions to “act immediately.” A fix for the third is still pending, according to Volexity.

    Volexity, which reported the flaws to Ivanti,

    This post was originally published on The Hacker News.

    October 13, 2026
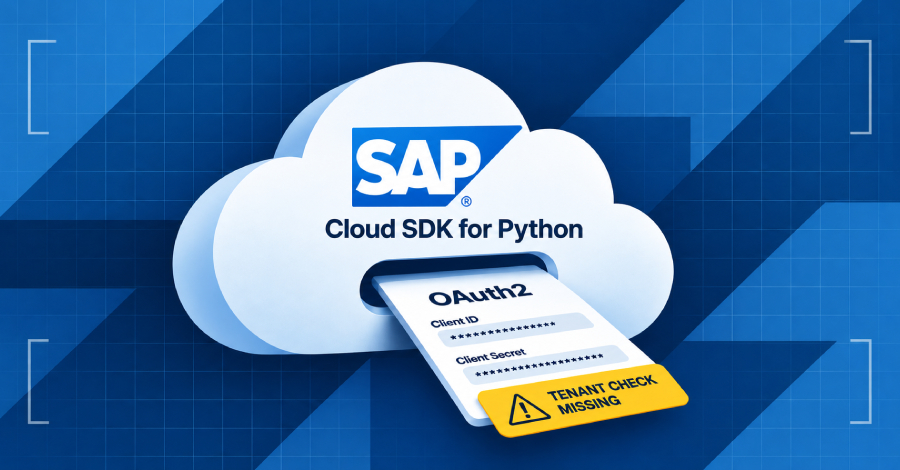
  • SAP Discloses Critical CVSS 10 Flaw in Cloud SDK for Python Allowing OAuth2 Credential Theft

    SAP Discloses Critical CVSS 10 Flaw in Cloud SDK for Python Allowing OAuth2 Credential Theft

    A flaw in SAP’s Cloud SDK for Python can send an application’s OAuth2 client credentials to a server an attacker controls, SAP said in a security advisory on October 13. The flaw affects multi-tenant applications on SAP Business Technology Platform (BTP) that use the SDK, SAP’s official Python client for BTP services. An attacker must be able to control the tenant subdomain,

    This post was originally published on The Hacker News.

    October 13, 2026
  • TFG London cyberattack disrupts systems at Hobbs and Whistles retailers

    TFG London detected a cybersecurity incident that impacted IT systems used by the Phase Eight, Hobbs, and Whistles premium fashion brands. […]

    This post was originally published on BleepingComputer.

    October 13, 2026
←Previous Page
1 2 3 4 … 33
Next Page→

proxyblue.yourcyber.news

  • Blog
  • About
  • FAQs
  • Authors
  • Events
  • Shop
  • Patterns
  • Themes

Twenty Twenty-Five

Designed with WordPress