Skip to content

proxyblue.yourcyber.news

  • GitHub Tightens npm Publishing After Flaw Left 1,500+ Packages Vulnerable to Hijacking

    GitHub Tightens npm Publishing After Flaw Left 1,500+ Packages Vulnerable to Hijacking

    GitHub has taken the step of expiring unvalidated npm trusted publishing configurations 48 hours after creation after researchers found that it was possible for an attacker to push new versions of a different user’s package without having to steal their credentials.

    “Your configuration becomes validated and exempt from expiry after its first successful publish,” the Microsoft-owned subsidiary

    This post was originally published on The Hacker News.
    October 13, 2026
  • Ivanti warns of Connect Secure zero-day exploited in attacks

    Ivanti urged customers on Tuesday to immediately patch an actively exploited zero-day vulnerability in the Ivanti Connect Secure (ICS) remote access gateway. […]

    This post was originally published on BleepingComputer.

    October 13, 2026
  • Docker Hub flaw let attackers impersonate users, tamper with images

    Docker has disclosed a critical vulnerability (CVE-2026-105445) in Docker Hub that let attackers access another user’s container repositories using a personal access token (PAT). […]

    This post was originally published on BleepingComputer.

    October 13, 2026
  • Dangerous flaws in refrigeration equipment were disclosed months before retail attacks

    Dangerous flaws in refrigeration equipment were disclosed months before retail attacks

     Hundreds of French supermarkets faced a sophisticated hack where industrial controls were manipulated.

    This post was originally published on Cybersecurity Dive.

    October 13, 2026
  • Businesses need more integrated risk management to counter cyberattacks, AI-powered fraud

    Businesses need more integrated risk management to counter cyberattacks, AI-powered fraud

    Risks are growing at a time when companies are relying more than ever on vendors for cybersecurity, according to a new report.

    This post was originally published on Cybersecurity Dive.

    October 13, 2026
  • The MFA Gaps Attackers are Still Exploiting

    Attackers continue exploiting gaps in MFA coverage, using stolen credentials to access VPNs, RDP, and Windows systems that still rely on passwords alone. Specops explains why protecting cloud applications isn’t enough and how organizations can close these authentication gaps. […]

    This post was originally published on BleepingComputer.

    October 13, 2026
  • SAP warns of maximum severity OAuth2 SSRF security flaw

    SAP has addressed 20 security flaws across multiple products in its October 2026 security updates, including a maximum-severity vulnerability in the Cloud SDK for Python. […]

    This post was originally published on BleepingComputer.

    October 13, 2026
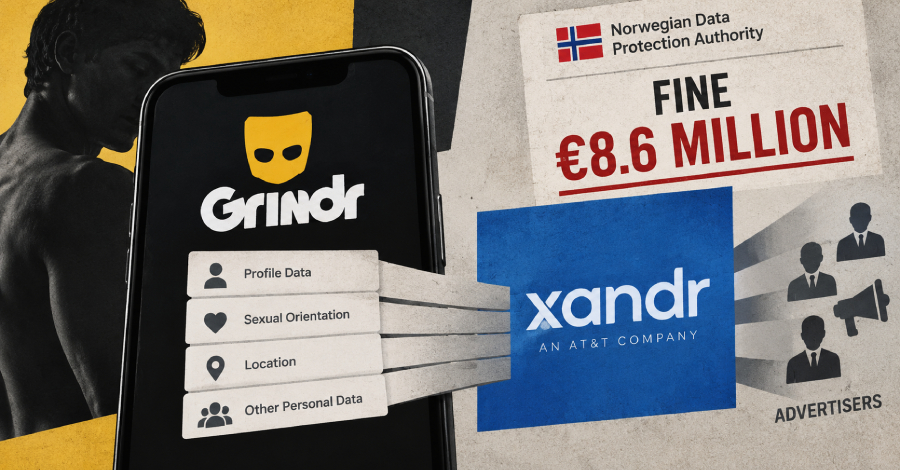
  • Xandr Fined a Record €8.6 Million for Relaying Grindr Data Revealing Sexual Orientation

    Xandr Fined a Record €8.6 Million for Relaying Grindr Data Revealing Sexual Orientation

    The Norwegian Data Protection Authority (DPA) has fined Xandr, an advertising unit owned by Microsoft, €8.6 million ($9.62 million) for illegally relaying ​Grindr users’ sensitive data to advertisers.

    The administrative penalty is the largest issued by the data protection watchdog, arguing the case merited a high fine because of the “very serious” nature of the breach. The infringements

    This post was originally published on The Hacker News.
    October 13, 2026
  • [Webinar] How to Stop AI-Driven Privilege Escalation With Runtime Identity Controls

    [Webinar] How to Stop AI-Driven Privilege Escalation With Runtime Identity Controls

    The dangerous part of a stolen identity isn’t always the initial login. It’s what an attacker can do with that access next.

    With AI accelerating reconnaissance, exploitation of vulnerabilities, and privilege escalation, attackers can move through systems faster than security teams can investigate. A compromised account that looks legitimate at first could become the starting point for a much

    This post was originally published on The Hacker News.
    October 13, 2026
  • LG Smart TVs Vulnerable to Pre-Auth Root Takeover From Local Network

    LG Smart TVs Vulnerable to Pre-Auth Root Takeover From Local Network

    Three vulnerabilities in LG’s webOS can be chained to give an attacker on the same local network root access to certain smart TVs without a PIN or any interaction from the owner.

    LG has issued a fix, according to an advisory published by SSD Secure Disclosure on October 12.

    The chain was tested on two TV models, the 32LQ636BPSA and the 27TQ600SW, running webOS 7.5.7-25 on firmware

    This post was originally published on The Hacker News.
    October 13, 2026
←Previous Page
1 2 3 4 5 … 33
Next Page→

proxyblue.yourcyber.news

  • Blog
  • About
  • FAQs
  • Authors
  • Events
  • Shop
  • Patterns
  • Themes

Twenty Twenty-Five

Designed with WordPress